
Sensitive Data Discovery Across Your Environment
What Seeker Can Scan
Seeker supports multiple scan methods so administrators can use the approach that best fits each data source.
- Local Drives & SMB File Shares: Scan local drives and accessible Windows/SMB shares for sensitive file content.
- Remote Windows Systems: Choose on-demand remote scanning without a permanently installed agent, or use Managed Seeker Agents for a permanent-agent deployment.
- Remote Mac Systems: Scan remote macOS systems using Seeker's remote Mac scanning workflow.
- Windows Search: Perform fast, index-based cursory scans of local or remote Windows systems, including indexed Outlook and OneNote content where available.
- Relational Databases: Scan Microsoft SQL Server, MySQL, Oracle, and PostgreSQL tables for sensitive information.
- Websites: Scan accessible website content using supported authentication methods.
- Microsoft OneDrive & SharePoint Online: Scan files stored in OneDrive and SharePoint Online for sensitive information.
- GitHub: Search public GitHub source code for credential-related exposure associated with your organization.
- Folder Permissions: Analyze NTFS folder permissions independently of content scanning.
Built-In and Custom Sensitive Data Detection
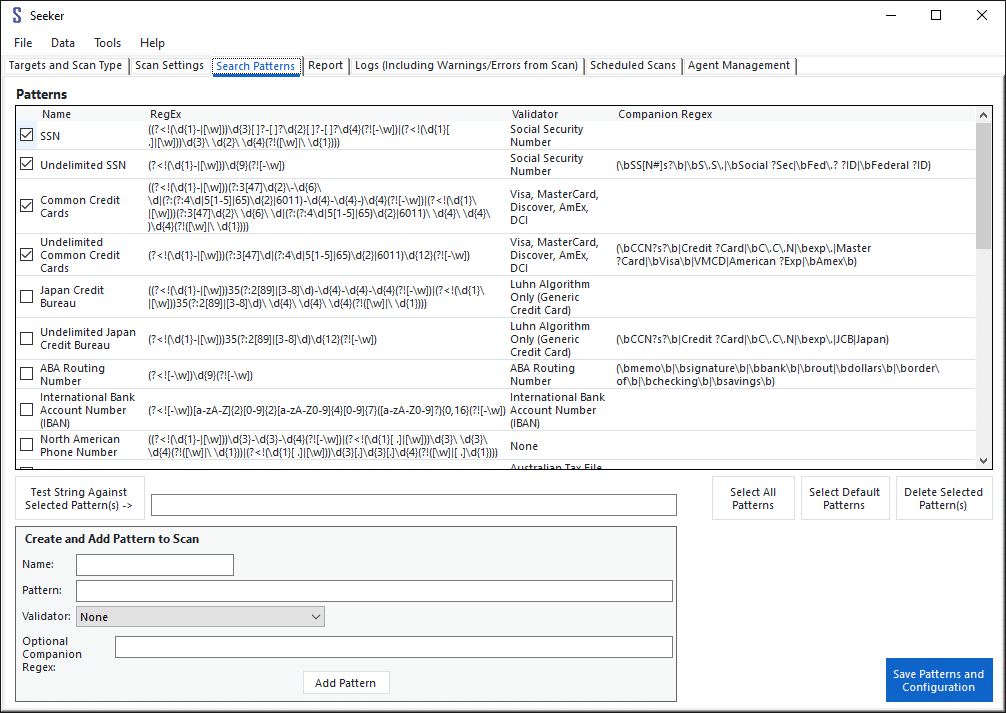
Seeker includes detection patterns and validators for common sensitive-data types and also supports custom regular-expression patterns for organization-specific needs.
SSNs • Payment Cards • Financial Data • Credentials • API/SSH Keys • International Identifiers • Custom Patterns
Administrators can use validators to reduce false positives, optional companion expressions to add context, configurable match-display options, masking where applicable, file-extension controls, and path filters.
Broad File Format Support
For many common document types, Seeker uses Microsoft Windows IFilters to extract searchable text. IFilters are the same extensible filtering technology used by Windows Search and can provide more reliable extraction than treating complex files as plain text.
Seeker also includes internal extraction methods for additional formats, and organizations can install compatible IFilters for specialized file types used in their environments. Once the associated file extension is included in Seeker's scan configuration, an installed IFilter can be used during scanning.
Seeker also includes a file-type scanning test so administrators can verify that configured extraction prerequisites are working before a large scan.
Designed for Large-Scale Scanning
Seeker uses different scanning approaches depending on the target. File shares can be scanned concurrently from the console, supported remote systems can execute scanning closer to the data, databases can be scanned concurrently, and cloud and web sources use source-appropriate workflows.
The diagrams below illustrate several of these scanning approaches.
Concurrent Remotely Executed Scans

Concurrent SMB Scans

Concurrent Database Scans

OneDrive and Web Scanning

Understand Who Can Access Sensitive Data
Permission Alerts During Content Scans: Seeker can identify Windows file findings whose permissions match configured exposure conditions, helping administrators prioritize sensitive files that may be broadly accessible.
Explore Folder Permissions: Dedicated NTFS folder-permission scans let administrators review folder ACLs in a tree and grid interface, including Allow/Deny entries, common rights, inherited permissions, principals, and SIDs.
Permission analysis adds exposure context to discovery results without trying to replace a full Windows effective-access calculation.
From Discovery to Repeatable Operations
- Centralized Results: Review findings from scans across multiple source types.
- Historical Scans: Retain and reload previous scan results.
- Scheduling: Run recurring daily, weekly, or monthly scans.
- Dynamic Active Directory Targets: Re-resolve configured AD computer targets when scheduled scans run.
- Exclusions: Manage reviewed paths and file hashes to suppress unwanted findings.
- Flexible Result Storage: Use Seeker's encrypted local SQLite database or Microsoft SQL Server for centralized result storage.
- Command-Line Execution: Run saved scan definitions with SeekCL for automation workflows.
- Exports & Reports: Export findings for further review and remediation.
See Seeker in Your Environment
The best way to evaluate sensitive-data discovery is against your own systems and data sources.